External resource links and downloads open in a new tab.
As systems to control energy-using manufacturing equipment become more connected to the internet, it is important for plant operations staff to have an understanding of cybersecurity risks and to coordinate risk management activities within their organization.
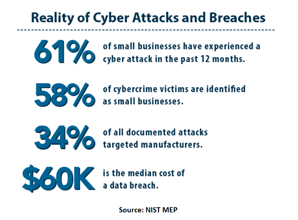
Small businesses may not consider themselves targets for cyber-attacks. However, they have valuable information cyber criminals seek, such as employee and customer records, bank account information, and access to larger networks. They can be at a higher risk for a cyber attack because they have fewer resources dedicated to security.
By addressing risk areas, you can protect your business from damage to information or systems, intellectual property theft, regulatory fines/penalties, decreased productivity, or a loss of trust with customers.
ITAC Cybersecurity Assessments
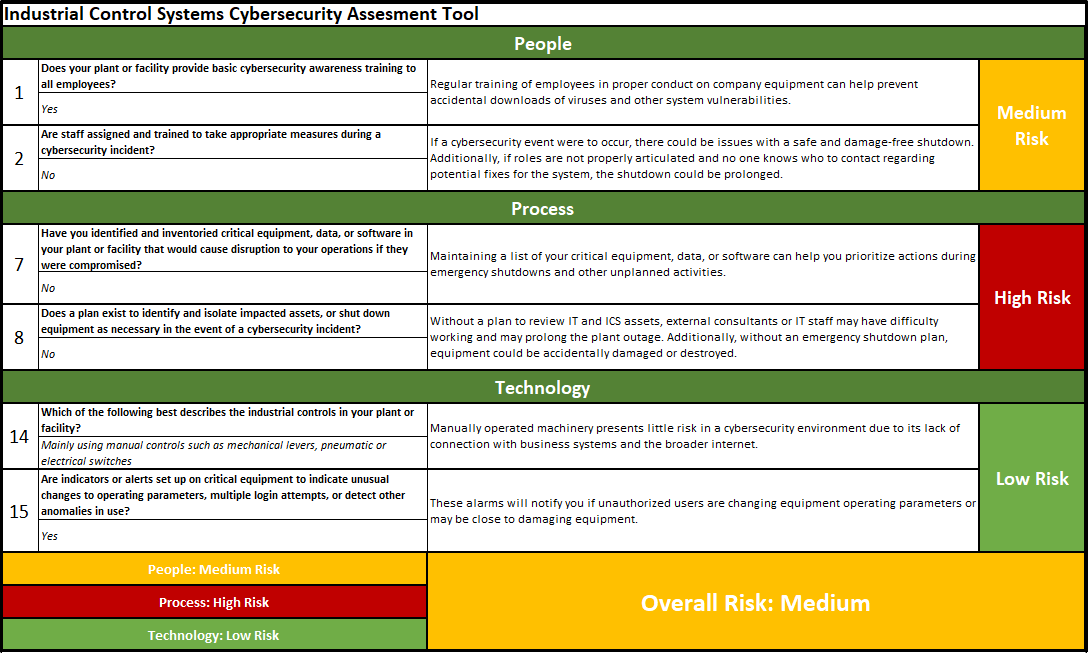
Industrial Training and Assessment Centers work with manufacturing clients to increase awareness of cybersecurity risks and potential mitigation activities. As part of facility site visits, ITAC clients may elect to receive cybersecurity risk assessments to identify security and privacy deficiencies to the business infrastructure, with a focus on vulnerabilities associated with industrial controls systems.
The ITAC Industrial Control Systems Cybersecurity Assessment Tool includes 28 simple questions to characterize industrial controls systems and plant operations. The tool then provides a high level assessment of risk (high, medium, or low). The companion User Guide provides additional context for the questions included in the tool, to help clients understand how certain business practices lead to cybersecurity risk. Upon conclusion of the assessment, the tool generates a customized list of action items associated with the risks identified. For additional guidance, ITACs refer clients to additional technical resource materials available through the NIST Manufacturing Extension Partnership (MEP) and other organizations.
To keep up with the growing need for cybersecurity in manufacturing ITAC has worked with NIST to update the Industrial Control Cybersecurity Assessment tool. The goal of this update is to help SMMs mitigate risk as they transition to Industry 4.0 standards. There are now additional questions related to access control of IT/OT infrastructure and cyber-physical systems.
ITAC Industrial Control Systems Cybersecurity Assessment Tool
Cybersecurity Fundamentals for Small and Medium Sized Manufacturers
Most plant operations managers are not cybersecurity experts, but can benefit from a basic understanding of cybersecurity risks and mitigation activities. A guidance document provided by NIST, NIST Small Business Information Security: The Fundamentals, provides a thorough and easily readable overview of cybersecurity basics.
As a first step, organizations need to understand their cybersecurity risks, to determine where the organization is vulnerable and may be subject to disruption of systems and processes. Organizations can use helpful checklists from the NIST document, or other cybersecurity assessment tools, to conduct the following activities:
- Identify what information your business stores and uses
- Determine the value of your information
- Develop an inventory of technologies used to store and process information
- Understand your threats and vulnerabilities
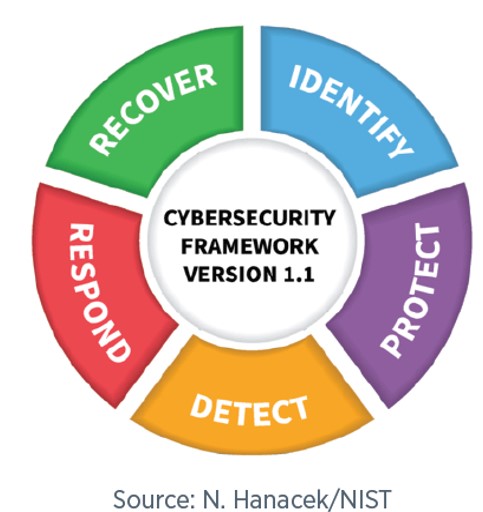
Once risks are understood, organizations can determine appropriate mitigation activities. Example activities are shown below, grouped into the five broad categories of the NIST Cybersecurity Framework:
IDENTIFY
- Identify and control who has access to your business information
- Conduct background checks
- Require individual user accounts for each employee
- Create policies and procedures for information security
PROTECT
- Limit employee access to data and information
- Install surge protectors and UPS
- Patch your OS and apps
- Install and activate firewalls
- Secure wireless access point
- Set up web and email filters
- Use encryption
- Dispose of old computers safely
- Train your employees
DETECT
- Install and update anti-malware
- Maintain and monitor logs
RESPOND
- Develop response plans
RECOVER
- Make backups
- Improve processes
Additional Cybersecurity Assessment Tools
Once an organization has a basic understanding of cybersecurity risks and vulnerabilities, a more detailed assessment can be used to determine mitigation actions and security controls. Some of the common tools used to perform assessments are listed below. The CSET tool is one of the more comprehensive tools available for small and medium-sized manufacturers. Organizations can explore resources available to help conduct assessments (e.g., ITACs, MEPs, third party vendors).
- Cyber Security Evaluation Tool (CSET): Comprehensive desktop software tool that guides users through a step-by-step process to assess their control system and information technology network security practices against recognized industry standards.
- NIST MEP Cybersecurity Assessment Tool: Online easy-to-use checklist that provides an assessment of business systems.
- Department of Energy C2M2 Model: Model used to measure the maturity of an organization’s cybersecurity capabilities, developed by energy sector subject matter experts.
- Department of Homeland Security Cyber Resilience Review: No-cost, non-technical assessment to evaluate an organization’s operational resilience and cybersecurity practices.
Additional Resources
National Institutes for Standards and Technology Manufacturing Extension Partnership (MEP)
Provides cybersecurity resources for small manufacturers, based on the NIST Cybersecurity Framework
Department of Homeland Security National Cybersecurity and Communications Integration Center (NCIC)
Provides resources focused on industrial controls systems